
Use Angular 22 injectAsync for genuinely optional services, avoid eager imports that collapse the split, choose a prefetch trigger, and verify the production bundle and network behavior.
Use Angular 22 injectAsync for genuinely optional services, avoid eager imports that collapse the split, choose a prefetch trigger, and verify the production bundle and network behavior.
Make the Key Vault authorization model explicit in Bicep, deploy the workload’s data-plane role, and verify secret access before a successful deployment hides a production 403.
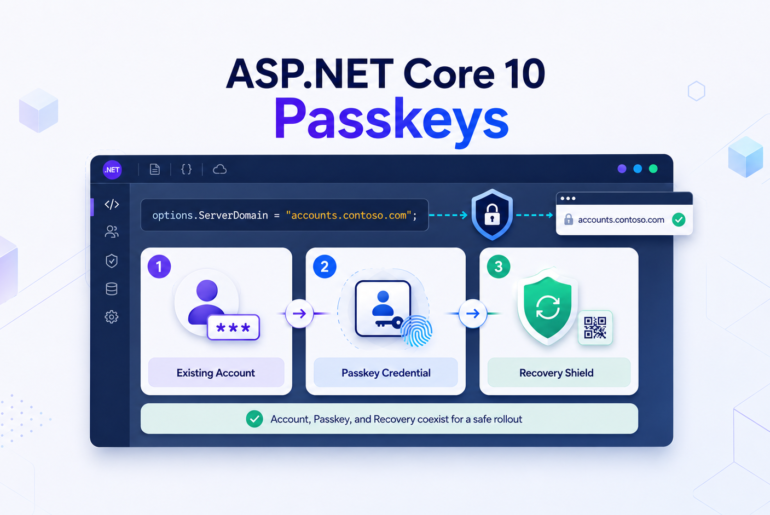
ASP.NET Core 10 passkeys can be added to existing Identity accounts without forcing an immediate passwordless migration. The safest approach…
.NET 10 NuGet Audit can make a CI restore fail because a package with a known vulnerability exists somewhere in…
Angular 22 OnPush behavior creates a migration split that is easy to miss: upgraded components can preserve Eager change detection,…
Microsoft.OpenApi CVE-2026-49451 can terminate an in-process parser when it receives a crafted OpenAPI document with circular schema references.If a security…
Three Angular security advisories affect SSR rendering, HttpTransferCache, and localized event-handler attributes. Learn which versions are vulnerable and how to audit and patch production applications.
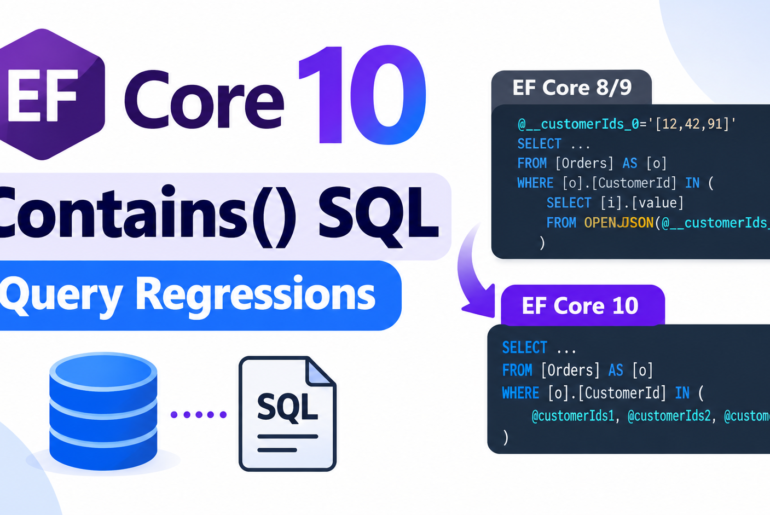
A LINQ query can look exactly the same after an EF Core upgrade while the SQL sent to the database…
.NET security updates are usually straightforward to install, but verifying that the patched runtime actually reached production takes a little…
Angular 22 Zoneless Reactive Forms can expose a subtle UI problem: the form model. changes correctly, but parts of the…
We have detected that you are using extensions to block ads. Please support us by disabling these ads blocker.
