
Keep direct MeterListener consumers working in .NET 11 by collecting observable HTTP metrics explicitly and verifying both client and server measurements.
Keep direct MeterListener consumers working in .NET 11 by collecting observable HTTP metrics explicitly and verifying both client and server measurements.
Use Blazor CacheView safely by choosing the correct vary-by dimensions, isolating per-request components, and testing that authenticated HTML never crosses user boundaries.
Keep direct MeterListener consumers working in .NET 11 by collecting observable HTTP metrics explicitly and verifying both client and server measurements.
Model fixed multi-shape JSON with C# 15 unions, resolve ambiguous reads, verify OpenAPI anyOf output, and protect ASP.NET Core clients before rollout.
Enable Angular 22.2 strictUnclaimedEventNames, verify NG8030 for a misspelled directive output, and enforce the compiler gate in CI.
Fix an ASP.NET Core and Angular 22 solution that receives API data but leaves the zoneless UI stale, then add signal state, DOM tests, and test-runner checks.
Add a post-build CI guard that verifies every local file referenced by Angular’s generated service-worker manifest across SSR and localized browser artifacts.
Use Angular 22 injectAsync for genuinely optional services, avoid eager imports that collapse the split, choose a prefetch trigger, and verify the production bundle and network behavior.
Angular 22 OnPush behavior creates a migration split that is easy to…
Three Angular security advisories affect SSR rendering, HttpTransferCache, and localized event-handler attributes. Learn which versions are vulnerable and how to audit and patch production applications.
Diagnose local DefaultAzureCredential timeouts, skip IMDS only in development, keep managed identity explicit in production, and verify the selected credential.
Diagnose Azure SQL error 13618, verify EF Core’s corrected OPENJSON translation, and keep an engine-backed regression test for native JSON columns.
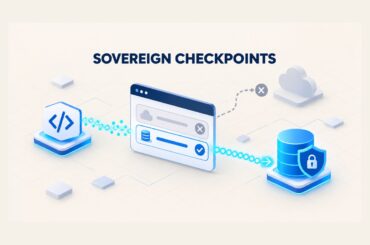
Upgrade the Event Hubs extension, prefer explicit storage service URIs, and prove that managed-identity checkpoints work in sovereign Azure clouds.
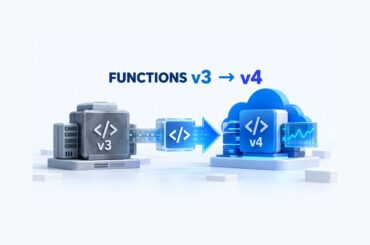
Migrate a C# Azure Functions v3 app on Linux Consumption to runtime v4, .NET 10 isolated, and Flex Consumption before the September 30, 2026 shutdown.
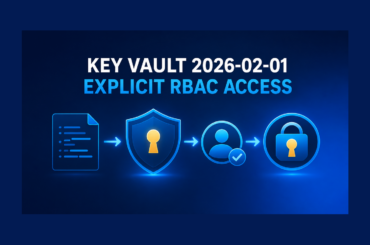
Make the Key Vault authorization model explicit in Bicep, deploy the workload’s data-plane role, and verify secret access before a successful deployment hides a production 403.
A reusable HttpClient service in ASP.NET Core should make the caller’s identity…
Fix BL0012 through BL0016 with production-focused component patterns, narrow suppressions, CI enforcement, and behavior checks for rendering, authentication, closures, and JavaScript interop.
Use the new .NET 11 Process signal and exit-status APIs to request graceful child shutdown, enforce a bounded wait, and preserve the real termination cause.
Enable CheckSdkVulnerabilities in .NET 11 CI, enforce NETSDK1238, NETSDK1239, and NETSDK1240, and avoid cache and global.json blind spots.
Audit the Configuration environment variable, pin every .NET CI command, and verify build, test, package, and publish handoffs before adopting .NET 11.
We have detected that you are using extensions to block ads. Please support us by disabling these ads blocker.