
Enable CheckSdkVulnerabilities in .NET 11 CI, enforce NETSDK1238, NETSDK1239, and NETSDK1240, and avoid cache and global.json blind spots.
Enable CheckSdkVulnerabilities in .NET 11 CI, enforce NETSDK1238, NETSDK1239, and NETSDK1240, and avoid cache and global.json blind spots.
Audit the Configuration environment variable, pin every .NET CI command, and verify build, test, package, and publish handoffs before adopting .NET 11.
Make .NET 11 SDK container publishes reproducible with SOURCE_DATE_EPOCH, verify identical registry digests, and diagnose legitimate input drift.
Inventory every self-hosted runner, query version-specific deprecation deadlines, and replace stale images before GitHub enforcement begins.
Audit JavaScript actions used by your .NET CI, force Node.js 24 across the workflow graph, and clear self-hosted runner blockers before September 23.
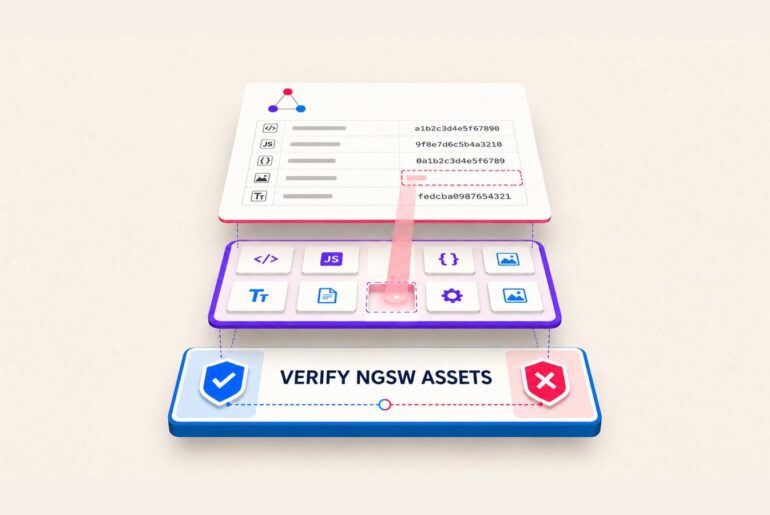
Add a post-build CI guard that verifies every local file referenced by Angular’s generated service-worker manifest across SSR and localized browser artifacts.
Use .NET 11 run-level timeout and maximum-failed-tests policies with Microsoft Testing Platform to bound multi-project CI time, noise, and failure cost.
Make the Key Vault authorization model explicit in Bicep, deploy the workload’s data-plane role, and verify secret access before a successful deployment hides a production 403.
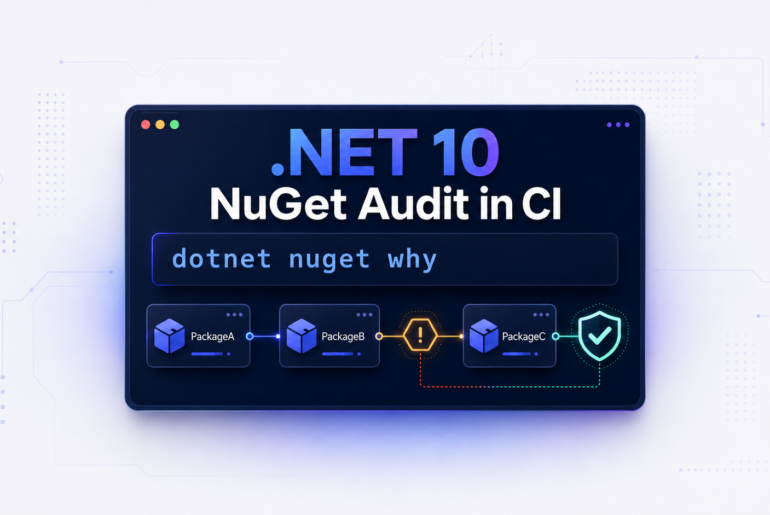
.NET 10 NuGet Audit can make a CI restore fail because a package with a known vulnerability exists somewhere in…
We have detected that you are using extensions to block ads. Please support us by disabling these ads blocker.
